An assistant that drafts text can often live inside a user's session. An agent that retrieves records, calls APIs, exchanges tokens, or triggers a workflow needs a different answer to a basic question: who acted, with what authority, and under whose direction?
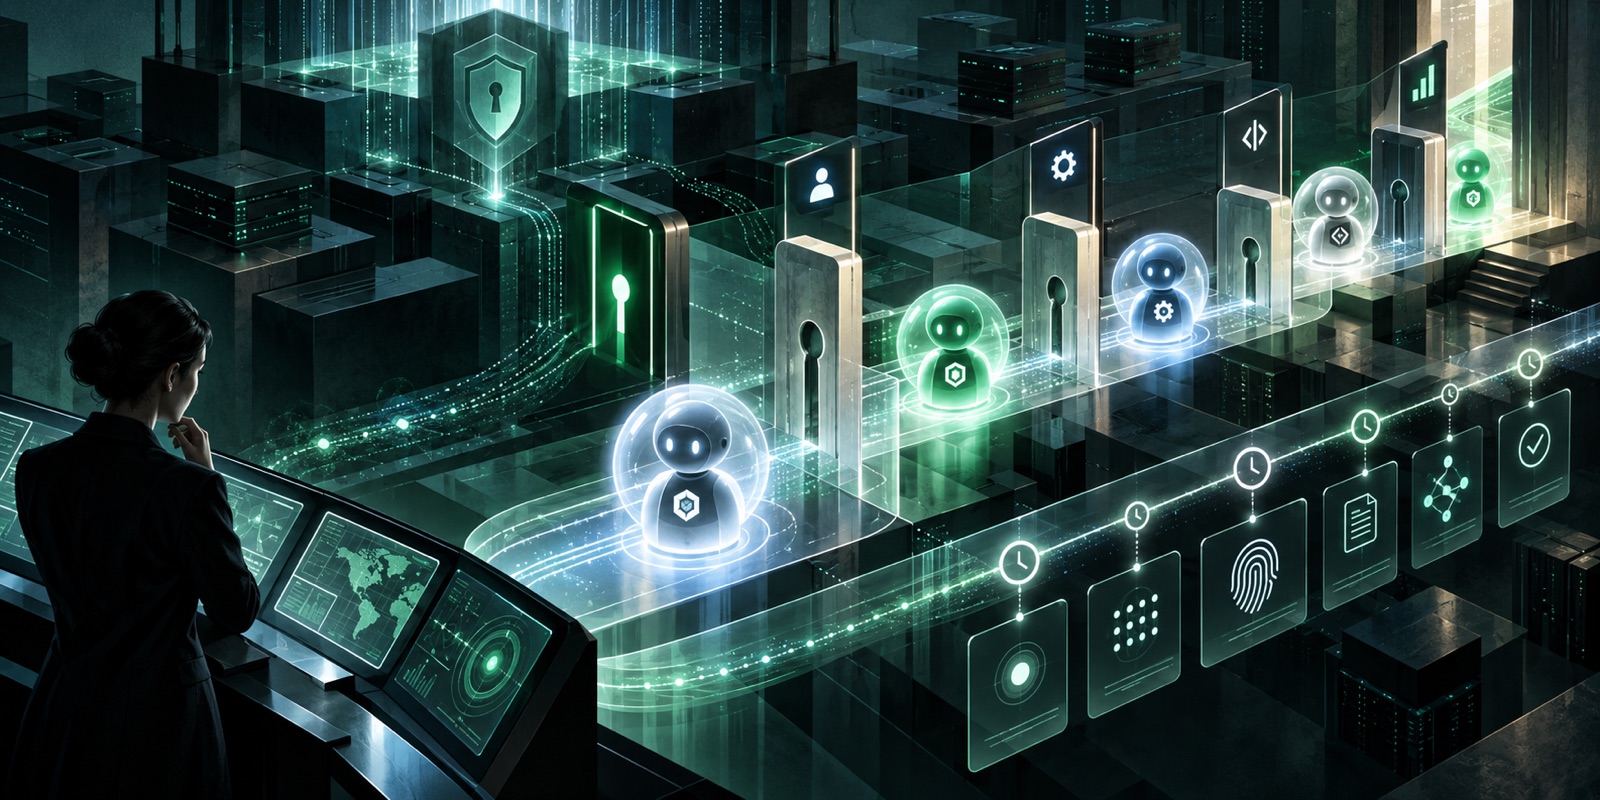
IBM's Agent Identity announcement puts that question at the center of its general-availability release. IBM describes a coordinated control plane for registering agents, recording ownership, preserving delegated authority, enforcing policy, protecting credentials, and connecting actions to an audit trail.
Identity has to survive the workflow
The hard part is not issuing an identity at the start of a session. It is carrying the chain through token exchanges, tool calls, downstream systems, and another agent. IBM emphasizes short-lived, task-scoped credentials and contextual authorization because a broad standing permission is hard to explain after something goes wrong.
Agent autonomy without an authority trail is just an unowned integration.
Small teams do not need an enterprise control plane on day one. They do need an owner, a bounded scope, a log of consequential actions, and a way to revoke access. Make those four things explicit before giving an agent a write capability, and the system has a chance to grow without losing accountability.
IBM describes an agent inventory, delegated access, contextual authorization, short-lived credentials, runtime controls, and correlated audit trails in the linked announcement.
IBM · Agent Identity is now generally available ↗